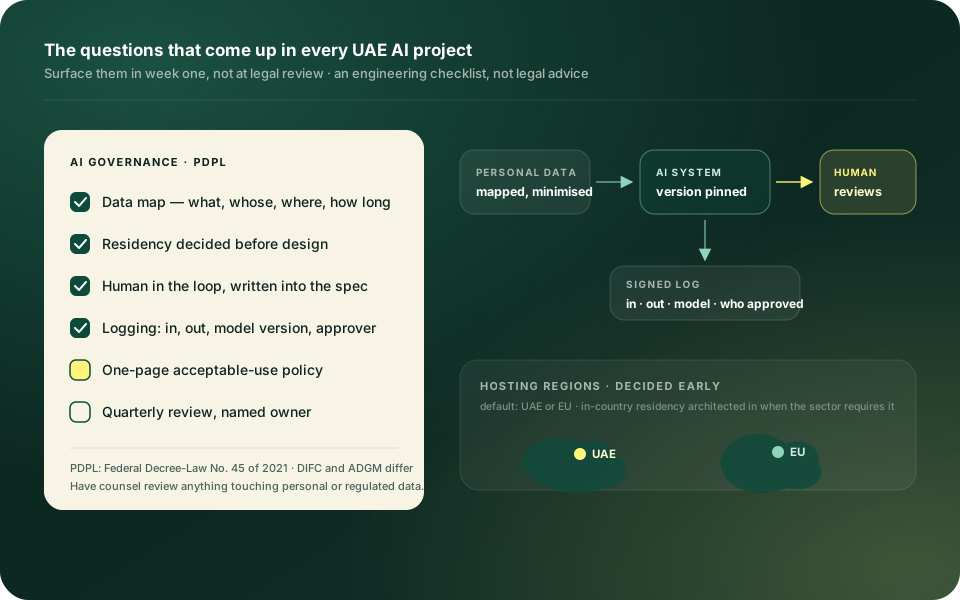
An AI governance checklist for a UAE business covers six things: a map of the personal data the system touches, hosting residency decided before design, human review defined for uncertain or consequential decisions, logging of inputs, outputs, model version and approver, a one-page acceptable-use policy, and a quarterly review with a named owner. It is an engineering checklist under the PDPL, not legal advice.
Start with the data map
What personal data touches the system, whose it is, where it is stored, who can see it, and how long it is kept. Most organisations discover during this exercise that the answer differs by department.
Residency, decided early
Where inference runs and where logs land are architectural choices. Changing them after launch is expensive. Free-zone regimes — DIFC and ADGM have their own data protection frameworks — may impose requirements that differ from the federal PDPL, so establish which applies to you before design.
Human in the loop, defined
Which decisions can the system make alone, which need review, and what happens when it is uncertain. Write this into the spec. 'The AI decides' is not a policy anyone will sign.
Logging and explainability
For any consequential decision, keep what went in, what came out, which model version produced it, and who approved it. Regulated sectors will ask. So will your own auditors.
An acceptable-use policy people will read
One page. What staff may put into public AI tools, what they may not, which approved tools exist, and who to ask. Long policies get ignored; that is the actual risk.
Review cadence
Models change under you. Quarterly review of accuracy, cost and edge cases, with a named owner. Set it up at handover or it won't happen.
The caveat
This is an engineering checklist, not legal advice. Have your counsel review any AI deployment that touches personal or regulated data.
Related services
Working on this in the UAE right now? We'll give you a straight read on your situation in 30 minutes.
Book a call